A Dobermann standing guard beside a cyber crime lab evidence report

WordPress maintenance for Cyber Essentials

Cyber Essentials evidence for your website

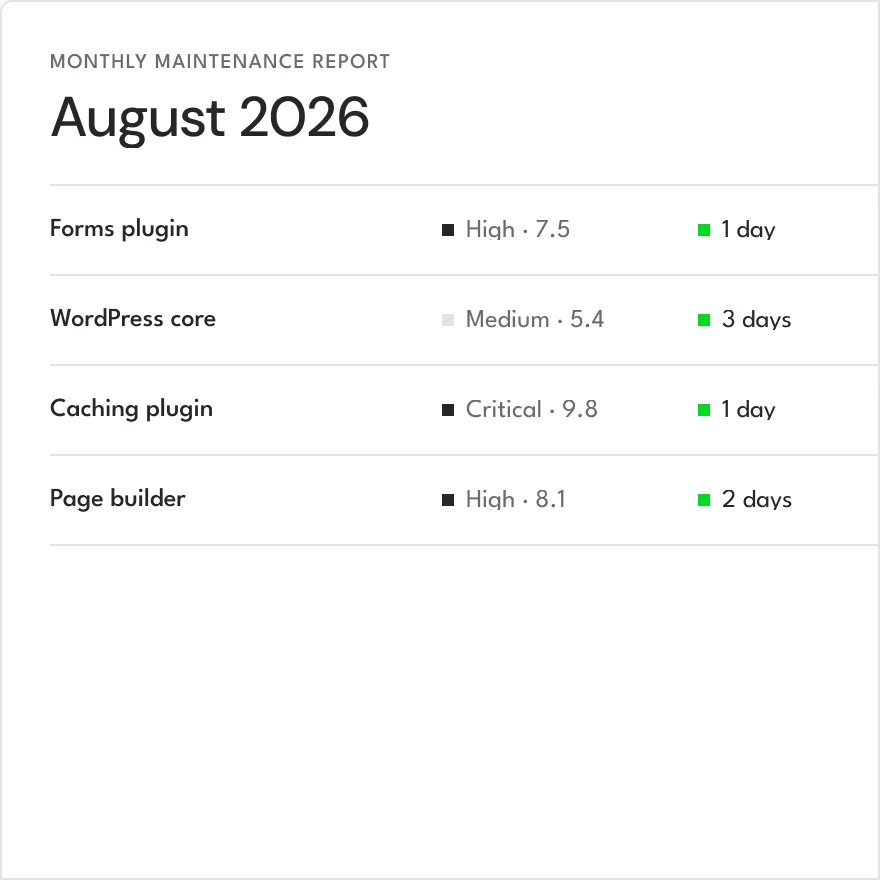
We hold the patching, the vendor support tracking, and the access controls on your WordPress site and send you a dated record every month. Next time somebody asks when the site was last patched, the answer is in front of you.

From $129 a month. Cancel monthly plans anytime.

Nobody counts the website as something that needs checking.

Worth looking at which application entries your last assessment listed and who was named against the site. In firms of your size, it is usually nobody, because your IT provider does not hold the website and never agreed to it.
A stethoscope on a green panel, checking the website like a health check

What we send you

Every month we send you a report of the work we did on your site.

What we patched, on what date, and on which plugin or theme. That is the document you hand an assessor. It is in every plan at no extra cost, and it starts arriving from your first month.

You are buying the record as much as the work.

The service

What we hold on your site.

Patching

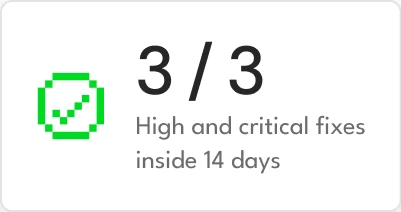
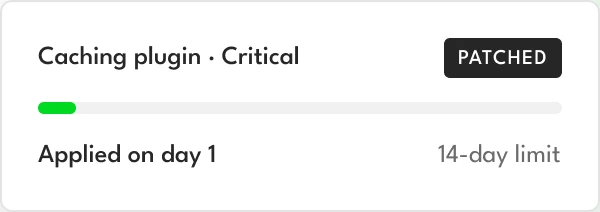
High-risk and critical updates shipped inside fourteen days, all year.

End-of-life tracking

Every plugin and theme is checked against vendor support, so an abandoned one is dealt with before an assessor finds it.

Access control

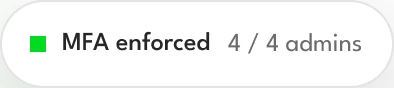
MFA enforced wherever it is available, our own admin access included.

Tested updates

Key pages checked before and after each update, rolled back if broken.

Malware scanning

Across the whole install, every 12 hours, with unlimited cleanups on annual billing.

Backups

Off-site, kept 90 days, with a second copy held by another company.

What it costs

Plans

The Standard

For businesses that need their site secured and off their plate.

$129 / month
Setup & migration$149 one-timeOn yearly billing: Free
Hack cleanup$50 per hourOn yearly billing: Free
Automated backupsDaily
Response commitment4 hours
Small jobs at onceOne
We test a real restore.Once a year
Start on this plan
Recommended

The Higher Standard

For sites where a slow page or broken form has a direct cost.

$249 / month
Setup & migration$149 one-timeOn yearly billing: Free
Hack cleanup$50 per hourOn yearly billing: Free
Automated backupsEvery 12 hours
Response commitment2 hours
Small jobs at onceTwo
We test a real restore.Twice a year
Start on this plan

The Highest Standard

For high-traffic or multi-location operations where the site is a core business asset.

$479 / month
Setup & migration$149 one-timeOn yearly billing: Free
Hack cleanup$50 per hourOn yearly billing: Free
Automated backupsEvery change, as it happens
Response commitment1 hour
Small jobs at onceThree
We test a real restore.Every 3 months
Start on this plan

Every plan carries the same protection. Higher plans back up more often, respond faster, take on more small jobs at once, and test a real restore more often.

Check maintenance plans
Cancel monthly plans anytimeSetup and migration free on yearly billing, $149 one-time on monthlyYour latest off-site backup is handed back when you leave.
A Dobermann walking through a narrow doorway

Who we work with

This is a narrow page, deliberately.

This is built for.

UK suppliers holding or bidding for in-scope central government work, running WordPress on paid infrastructure, where one person signs. If you hold Plus, more so.

This is not for.

Suppliers with an in-house security function that already owns the certification. Anything inside a group where certification is handled centrally. Anything where a bid team runs the conversation rather than the owner.

Stop finding out by asking someone else.

We handle setup and migration for you, free on yearly billing and $149 one-time on monthly. Change plans or cancel any time.

Onboarding

Onboarding takes 24 to 48 hours.

Your site stays live through onboarding.

Your first report date is named before you sign.

Common Questions

Publicly available commercial web applications are in scope by default, and bespoke components are out. Reading a licensed WordPress install as in scope is our reading of that wording, not a worked example in the document, and it is finally your assessor's call. We document the position either way.
High-risk and critical fixes for applications, including associated files and extensions. The trigger is a CVSS v3 base score of 7.0 or above, a vendor rating of high or critical, or a fix where the vendor gives no severity at all. A configuration change counts as a fix.
The question set. Certification bodies report that non-compliance on the security update question now fails an assessment on its own, regardless of performance everywhere else. Requirements for IT Infrastructure v3.3 and the Danzell question set apply to applications from 27 April 2026. Failing to use MFA where it is available fails on its own too.
No. PPN 014 says nothing about the public website, and its triggers relate to personal data and to ICT systems at OFFICIAL. The obligation reaches your site through the scheme's own software scope, not through procurement text.
Usually for devices, servers, and accounts. Worth checking which application entries your last assessment listed and who was named against the website. In smaller suppliers the answer is often nobody, because the provider does not hold the site.
Managed hosting normally covers the platform and the server. Plugins, themes, and the application layer usually sit with you, and under the scheme's shared responsibility treatment of cloud services that layer stays yours regardless of who hosts it.
It can, and the standard does not accept that as a reason to skip. Checking key pages before and after every update is how an update gets tested quickly rather than carefully. That is the service.
Plus adds independent hands-on testing, including an authenticated scan confirming nothing unpatched sits at CVSS 7.0 or above. That is where the site is tested rather than described, so the monthly record matters more, not less.
No. We hold no certification ourselves, and we won't tell you that you will pass or fail. We hold the clock, track vendor support across your plugins, and keep a dated record you can bring to assessment.
No. We maintain the one you already have. When something new needs building, the broader Pangolin team handles design, content, and SEO.